Apache-2.0 Rust · Pingora Self-hosted

Cloudflare-class protection for infrastructure you own

PingWAF is a distributed, centrally controlled Web Application Firewall. Define sites, rules and policies once in the control plane; every edge agent enforces them within seconds — no reload, no downtime.
Normalize → signatures → expressions → score
4 phases Normalize → signatures → expressions → score
gRPC control-plane protocol
7 RPCs gRPC control-plane protocol
DNS-01 ACME integrations
5 providers DNS-01 ACME integrations
SQLi · XSS · RCE · traversal
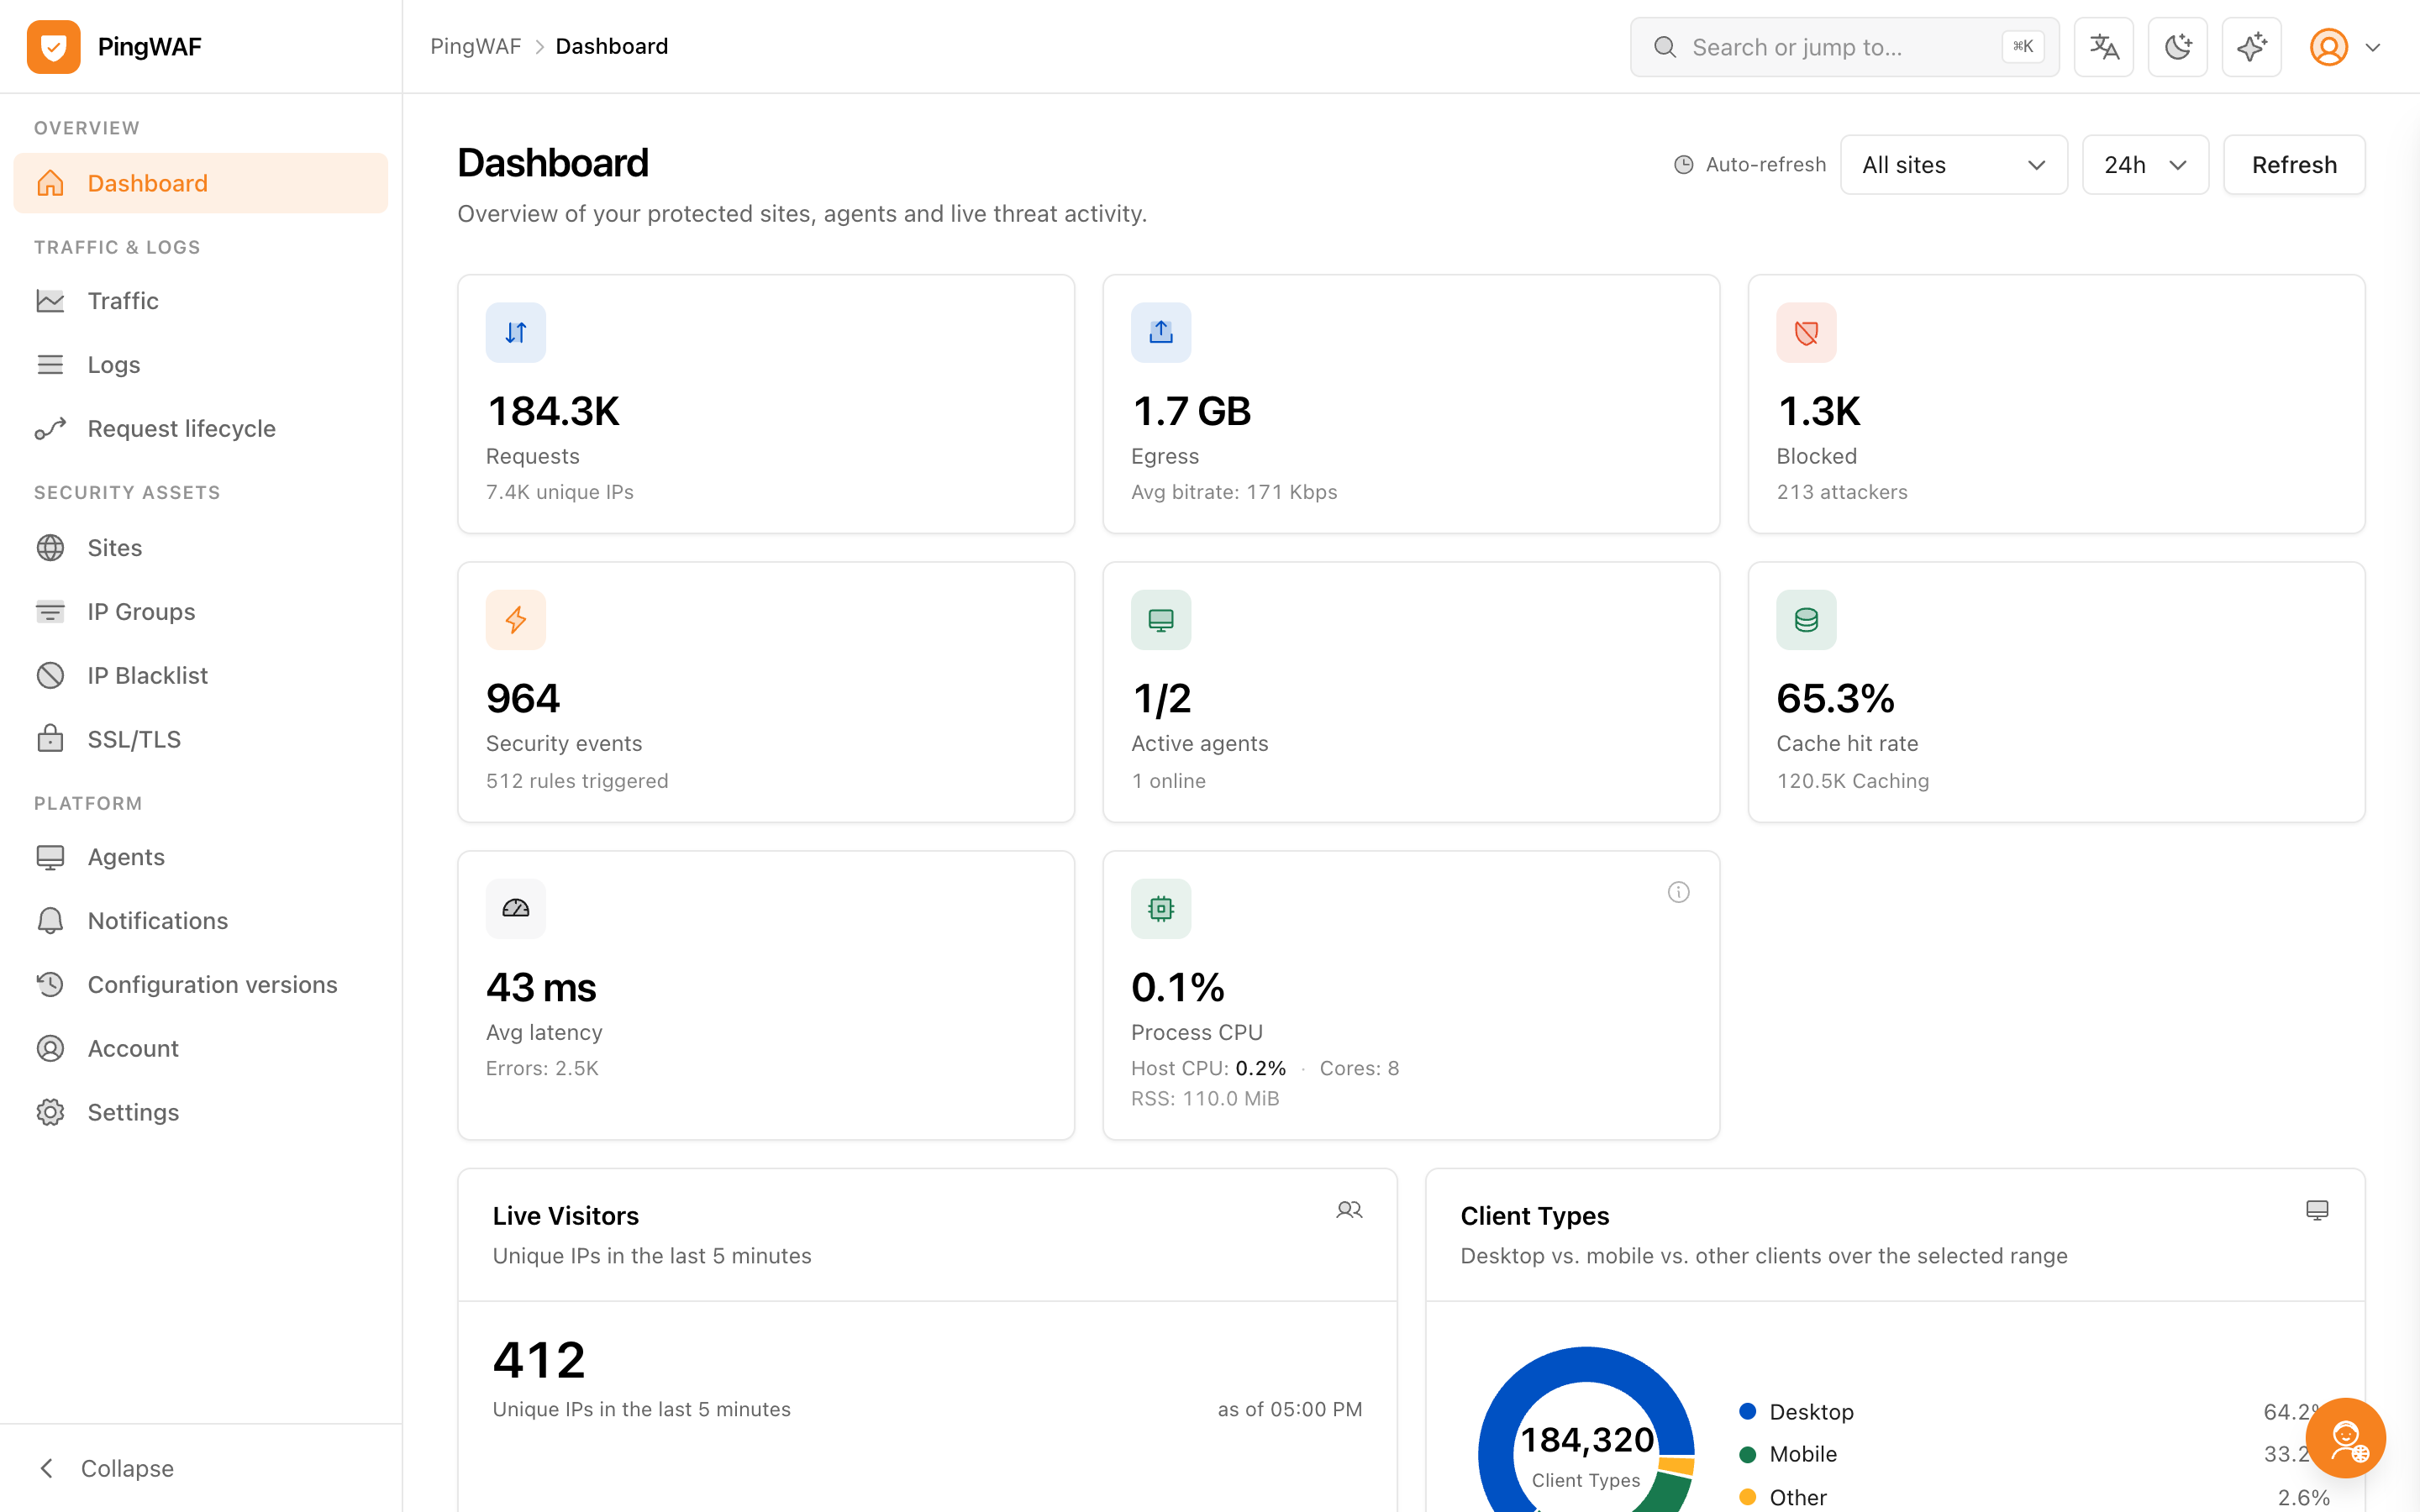
localhost:9080/dashboard
PingWAF dashboard with request analytics, attack trends and agent status
Rules pushed in seconds
Apache-2.0
Open source, end to end
No per-request pricing and no hosted dependency.
Rust
Memory-safe data plane
Pingora + tokio in one self-contained binary.
PostgreSQL
Control-plane state
Sites, rules, config snapshots and audit trail.
gRPC
Hot rule synchronisation
Bidirectional streams, no process restarts.

Architecture

One control plane, many edge agents

The control plane is the single source of truth for configuration. Agents only carry traffic and enforce policy, so you can scale the data plane without touching state.

The control plane owns state

Sites, rules, certificates and configuration versions live in PostgreSQL behind an Axum REST API, a tonic gRPC service and the embedded console.

Agents enforce at the edge

Each agent keeps a disk-backed rule cache and keeps serving with the last known policy even when the control plane is unreachable.

Changes land without a reload

SyncRules pushes a new bundle over the existing bidirectional stream; agents swap it in memory while requests keep flowing.

How the control plane works

Capabilities

Defense in depth, off by default

Every protection ships disabled and is enabled per site, so nothing changes your traffic behaviour until you ask it to.

Semantic WAF engine

Signature and heuristic detection for SQL injection, XSS, RCE, path traversal and command injection.

  • libinjection heuristics + Aho-Corasick matching
  • Cloudflare-style expression rules
  • Pass / Monitor / Block / Challenge verdicts
WAF engine

CC & bot defense

Absorb floods and separate real browsers from scripts with layered challenges.

  • JavaScript 5-second shield and proof of work
  • HMAC-signed clearance cookies
  • Verified-bot allow list per site
CC & bot defense

Access control

Decide who reaches the origin by address, region and request dimension.

  • IP rules with CIDR and CSV import
  • Geo blocks by country and ASN
  • Rate limits per IP, host, path or header
Access control

Traffic & caching

Route, balance and cache without leaving the console.

  • Origin pools with five balancing strategies
  • Prefix, exact and regex routes
  • Edge cache with quotas and SWR
Traffic & caching

TLS & certificates

Certificates issued at the edge and visible from one place.

  • ACME HTTP-01 and DNS-01 with renewal
  • Per-site certificate status in heartbeats
  • mTLS issuance and instant revocation
TLS & certificates

Observability & console

Every request is auditable, and every configuration change is reversible.

  • Request logs in Elasticsearch with WAL buffering
  • Raw request/response capture for replay
  • Config versioning with diff and rollback
Observability

All capabilities

Inside the console

Operations without a separate stack

The dashboard is compiled into the binary, so what you see is what the control plane knows.
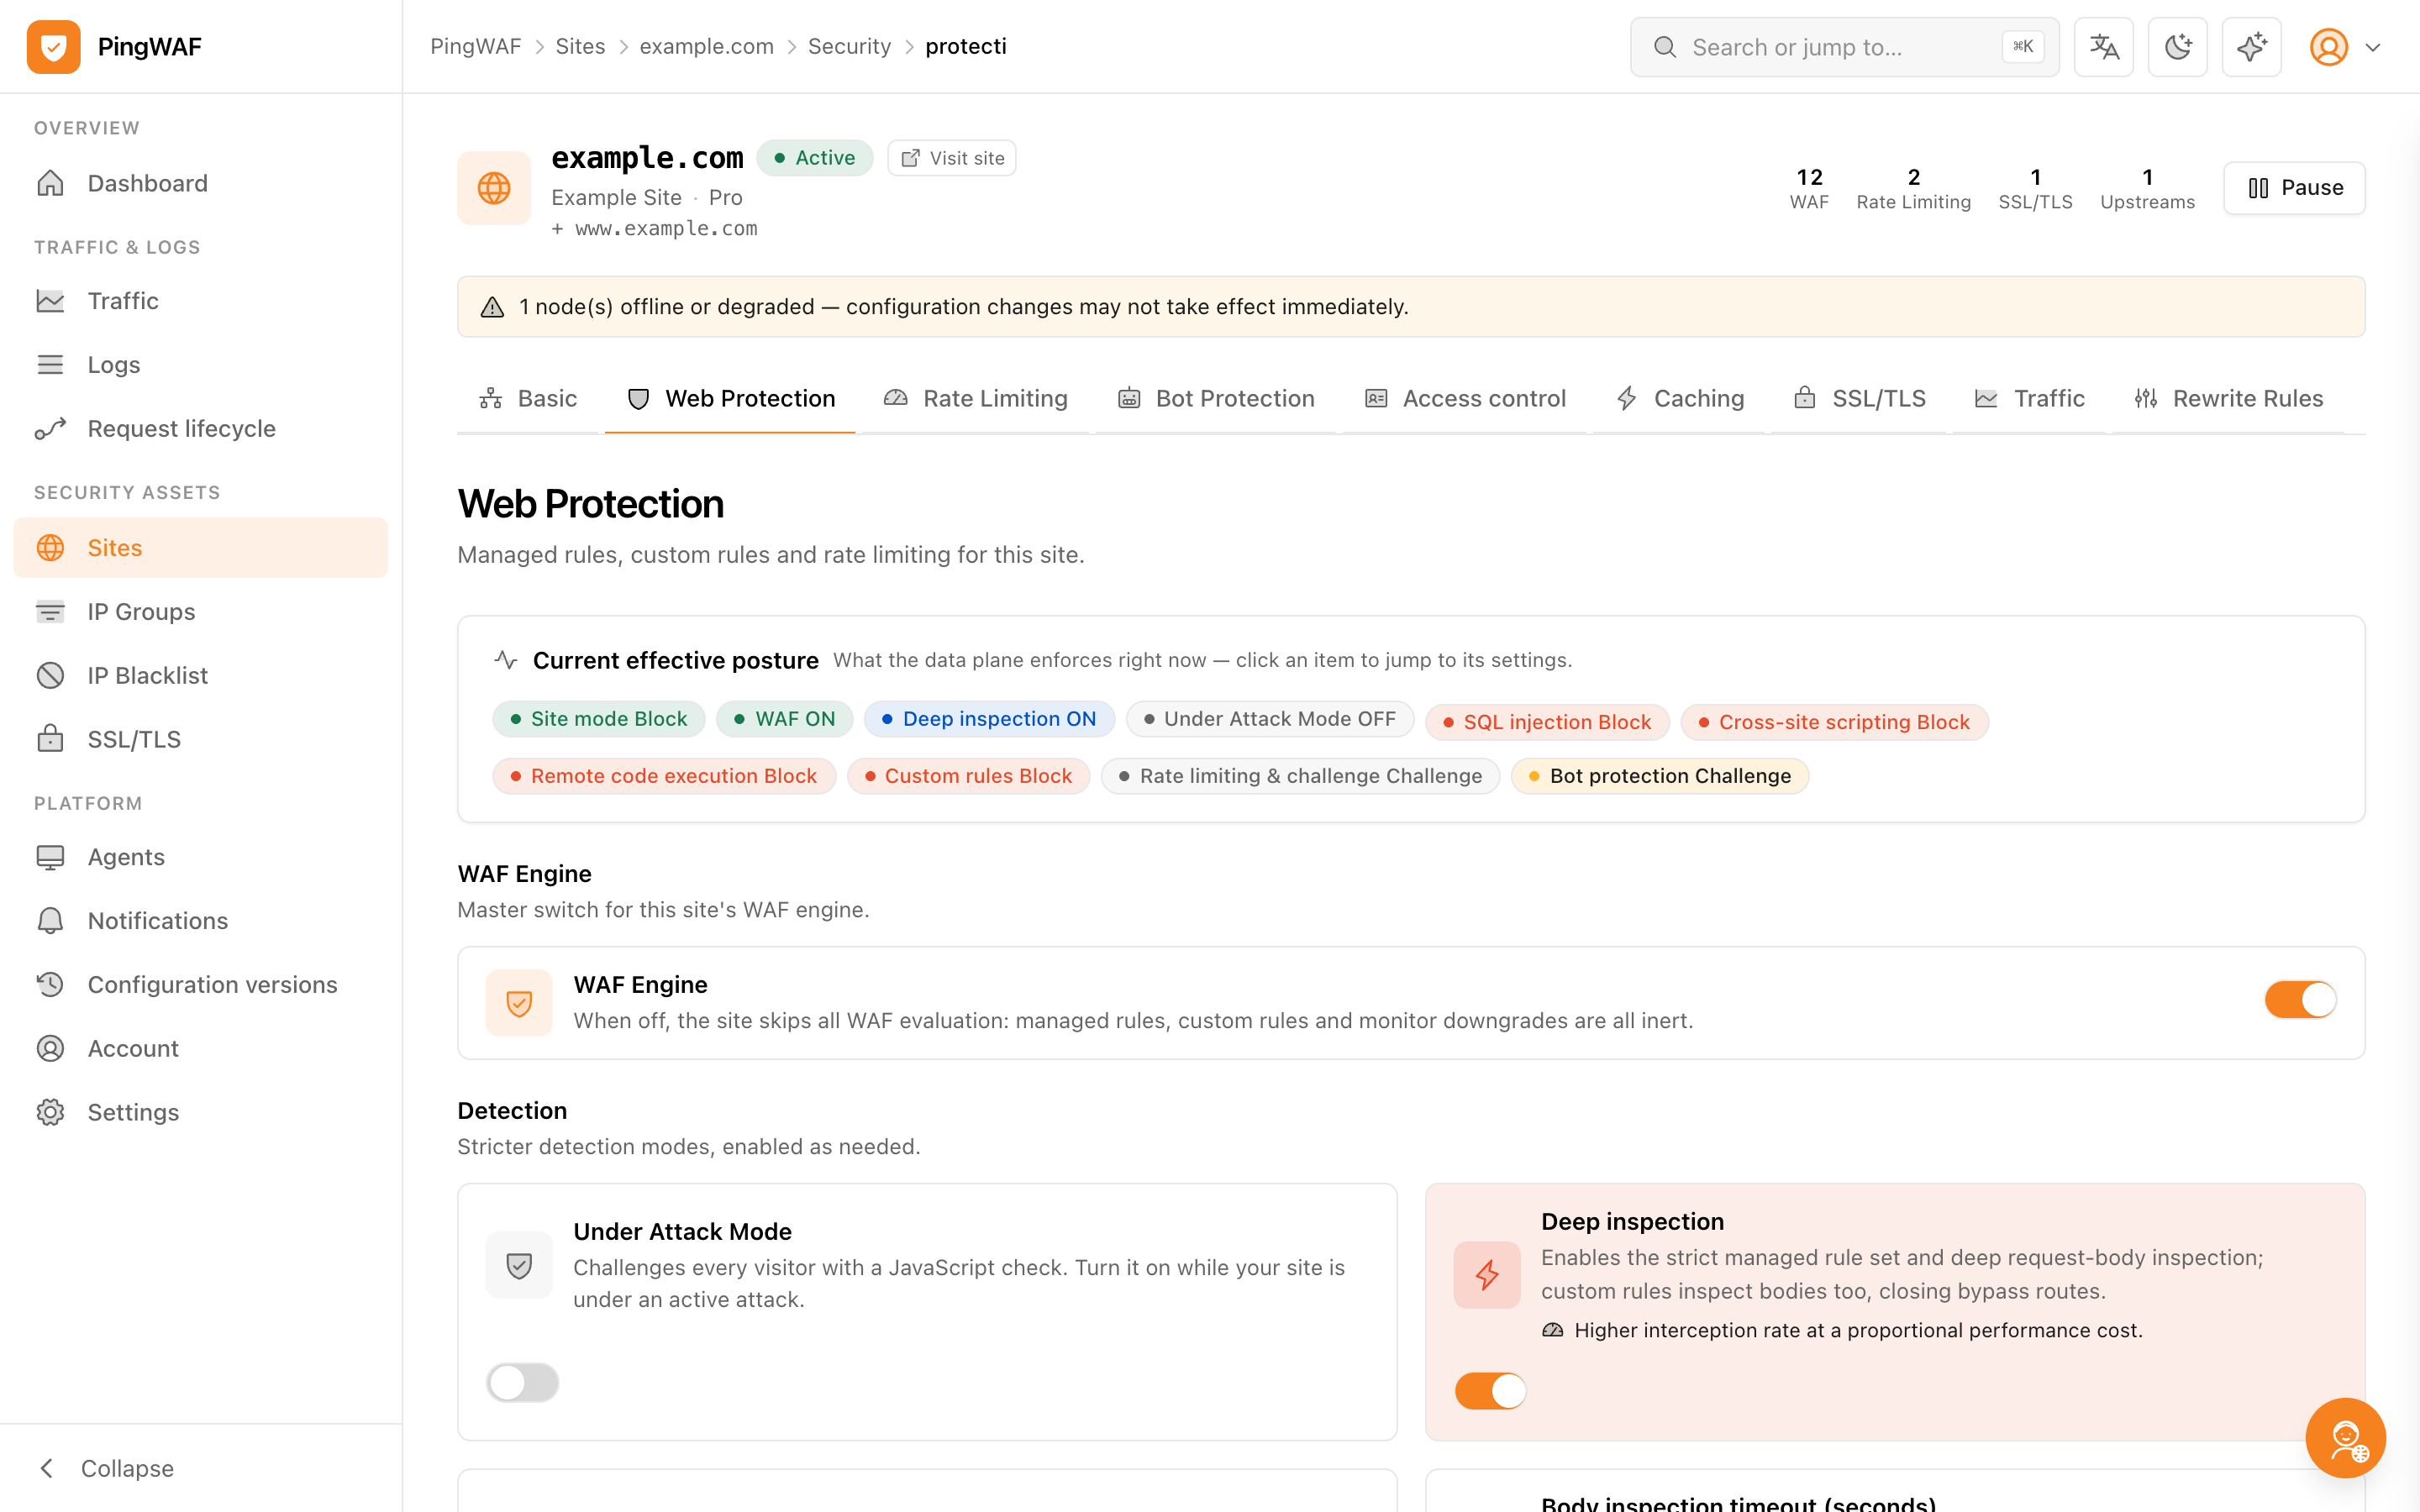
localhost:9080/sites/example.com/security/protection
PingWAF site protection page with WAF rule tabs and challenge settings
WAF rules and CC challenges are configured per site.
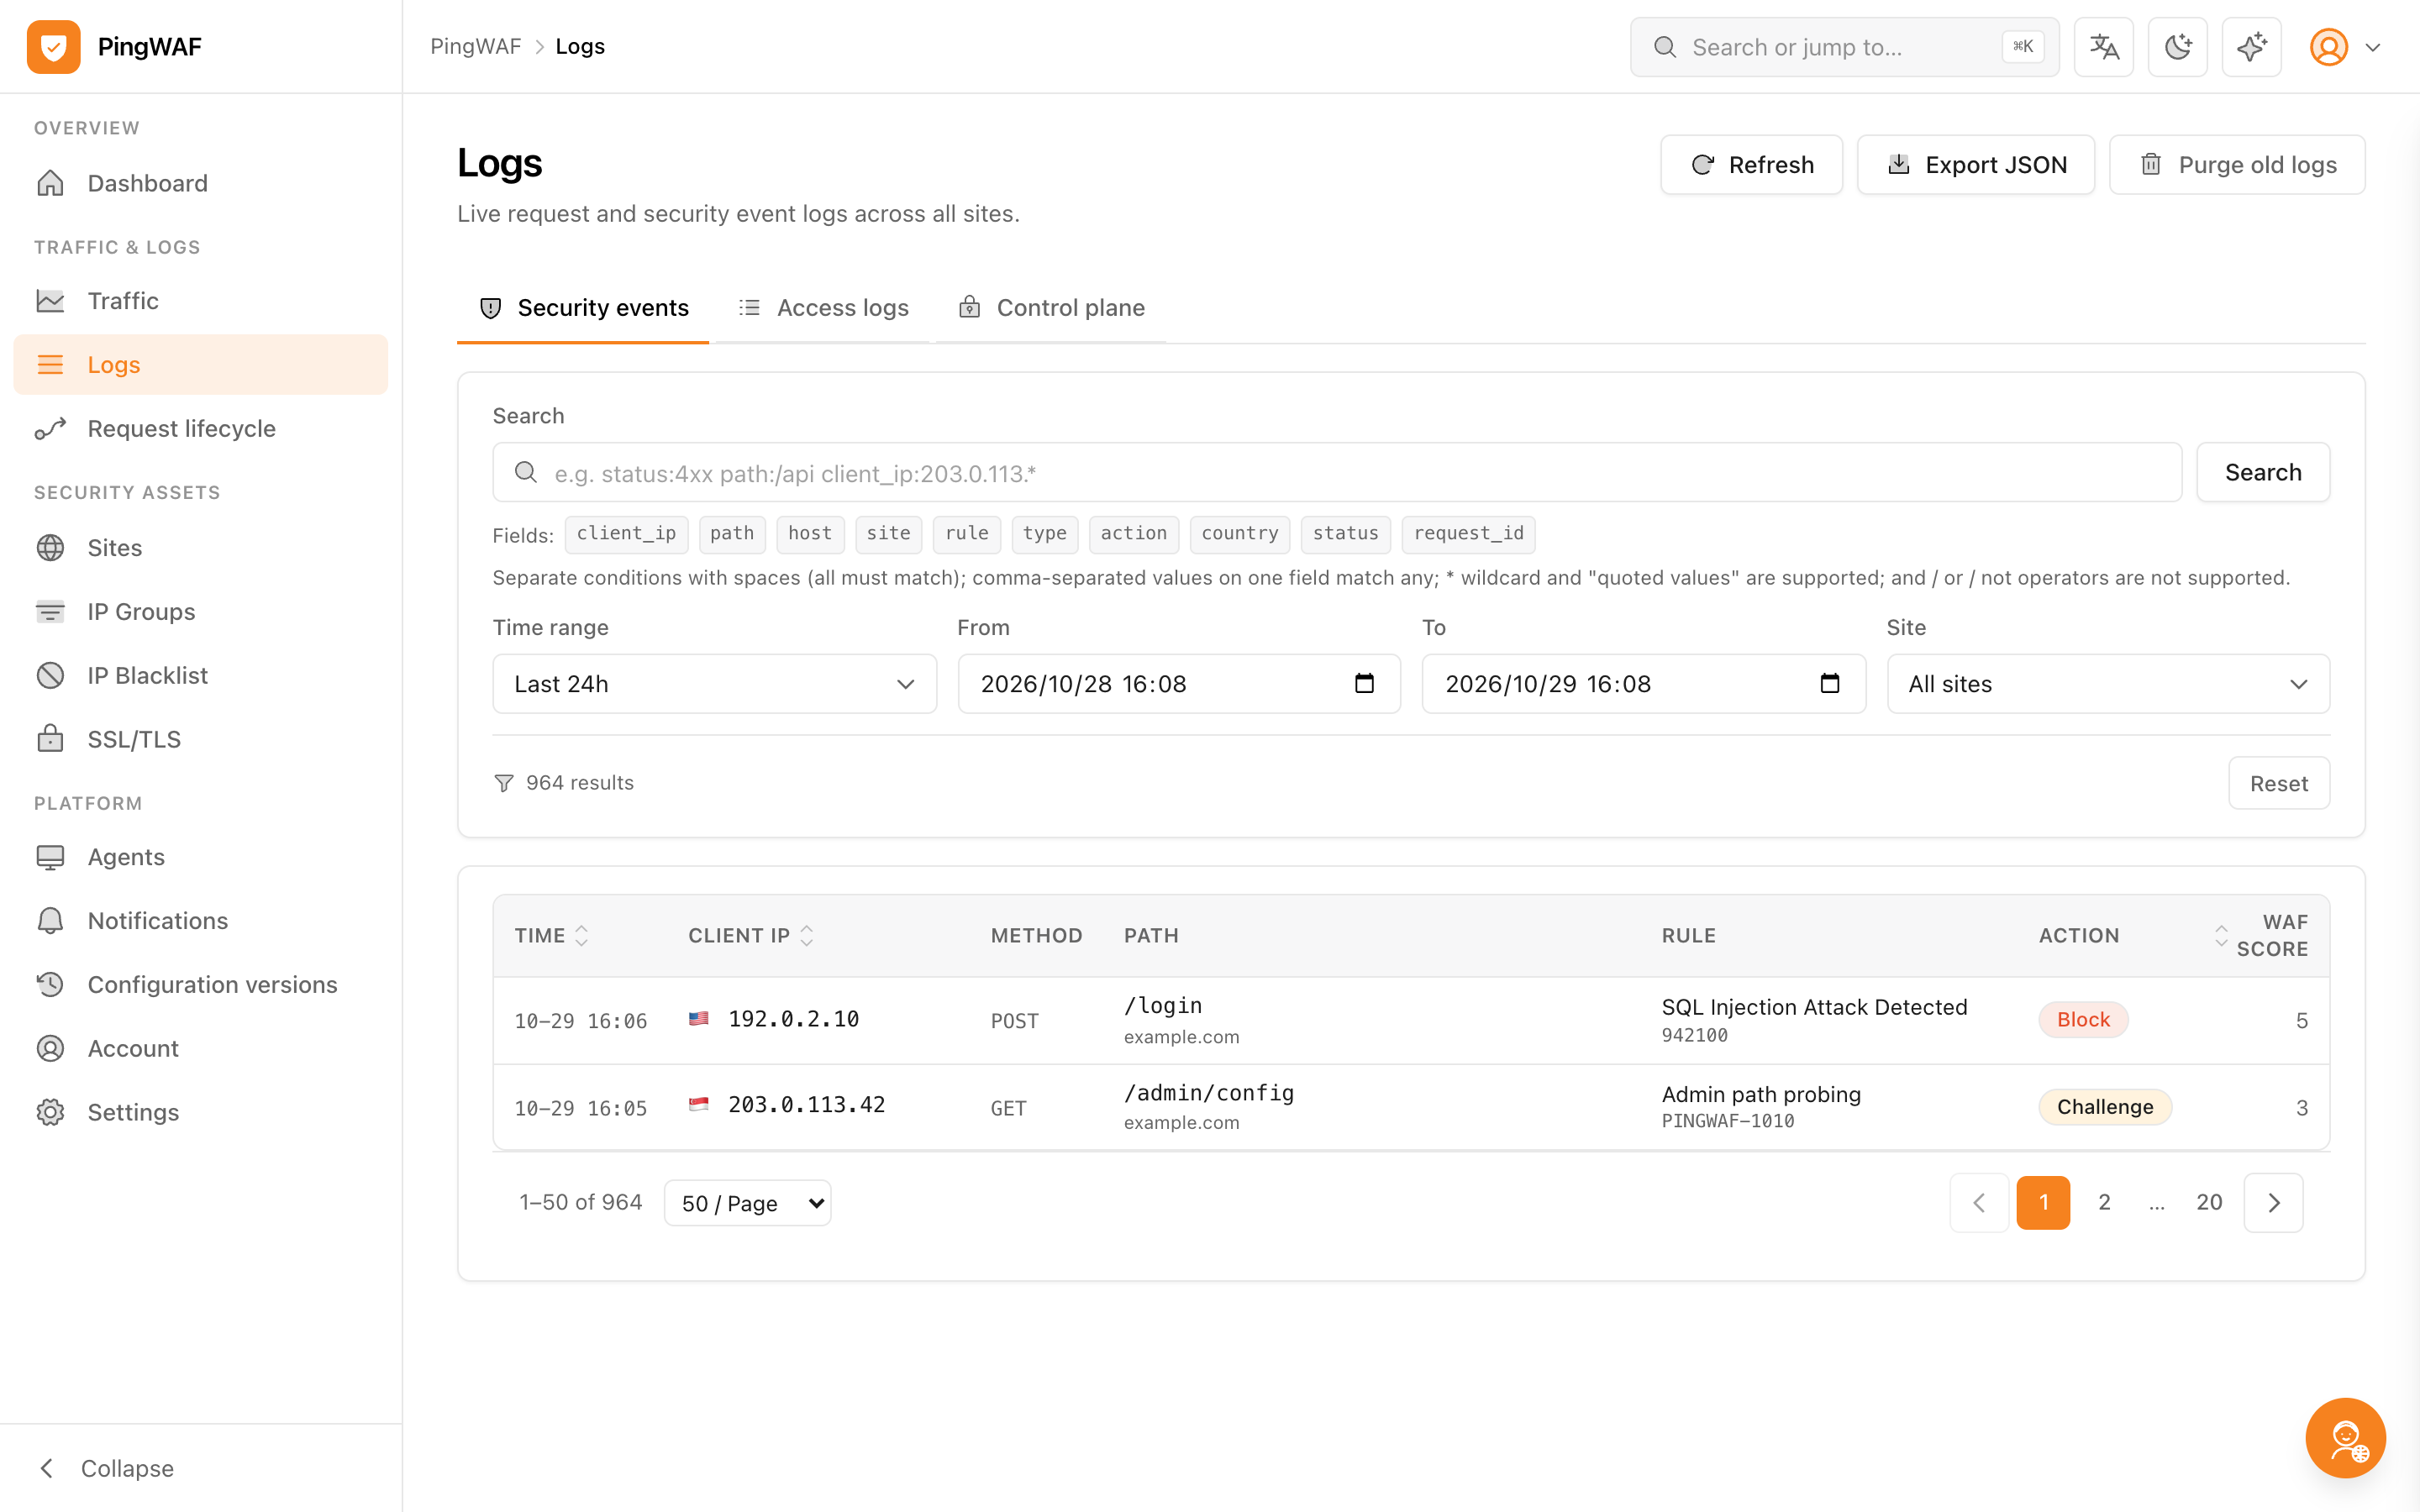
localhost:9080/logs
PingWAF request log list with verdicts and matched rules
Request logs carry the verdict, score and matched rule.
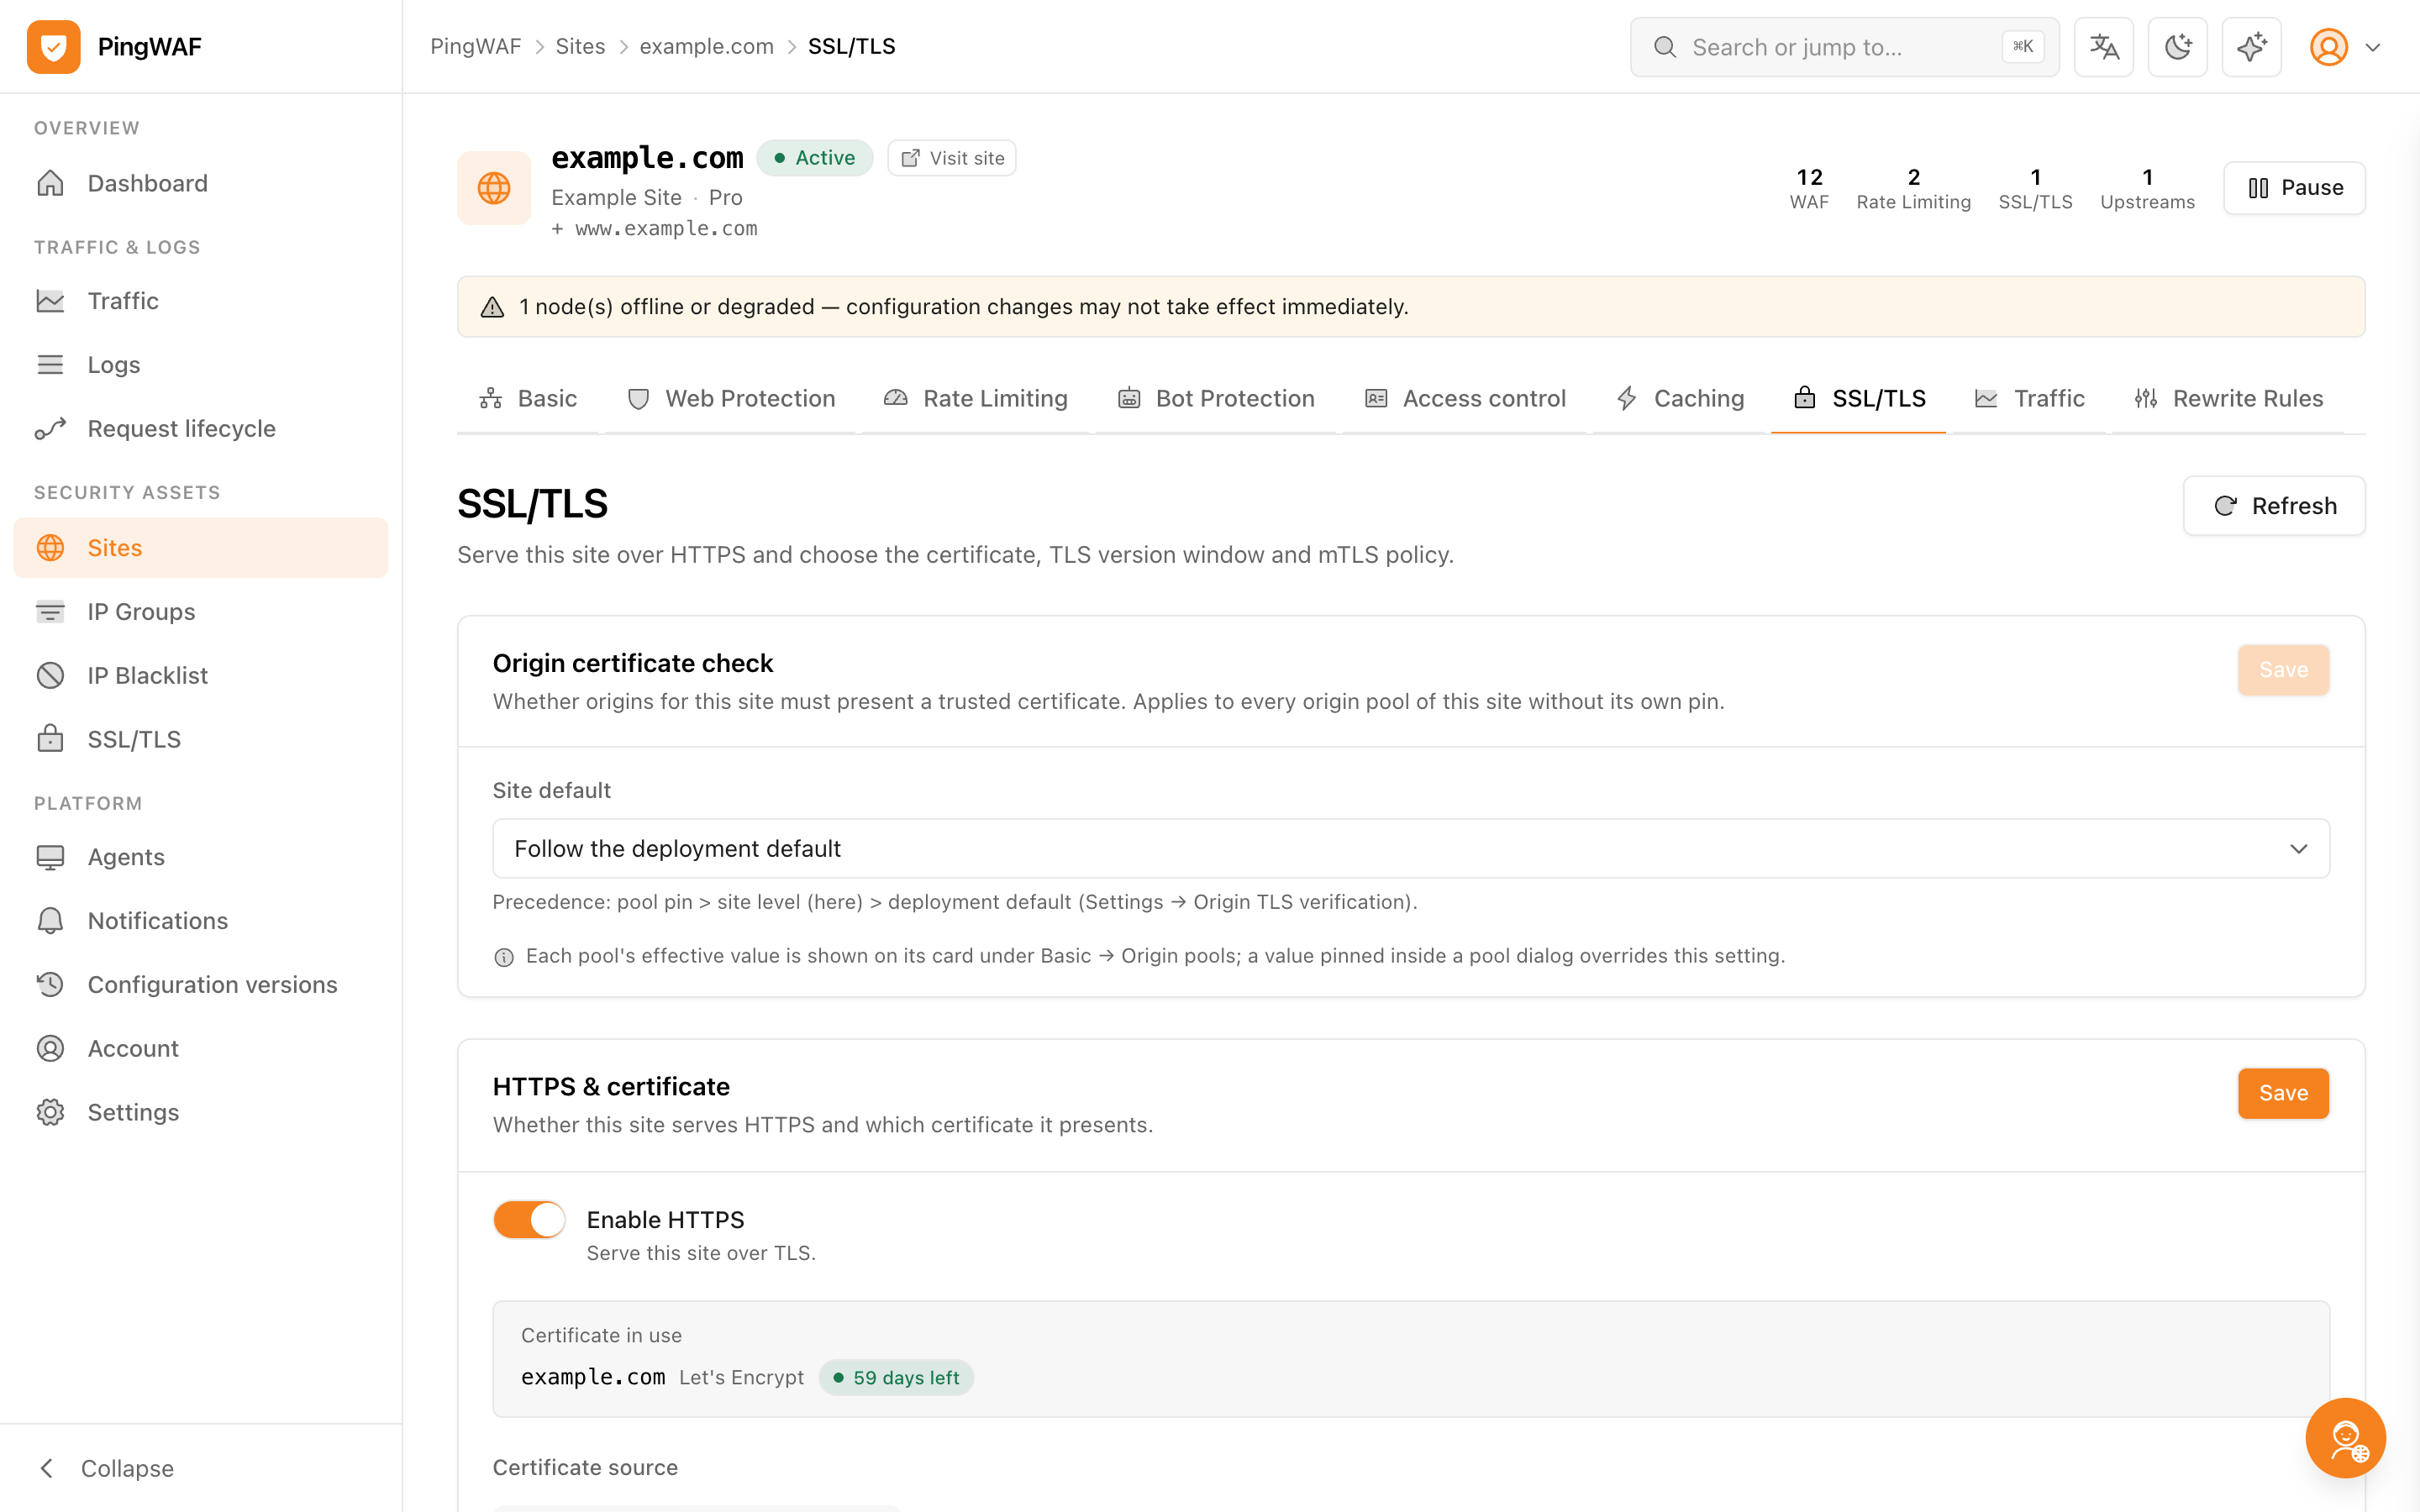
localhost:9080/sites/example.com/ssl
PingWAF site TLS page with certificate status and ACME events
Certificate status and ACME events for each site.

Quick start

From zero to a protected site

The bundled compose file starts the control plane, an agent and PostgreSQL. Sign in, add a site, and the edge starts enforcing.

  1. Start the stack

    docker compose up -d pulls the published image and starts PostgreSQL.

  2. Sign in

    Open https://localhost:9080 and use the seeded admin account.

  3. Add a site

    Point a hostname at the agent and enable protections per site.

bash — pingwaf
$ git clone https://github.com/shuaiZend/PingWAF.git
$ cd PingWAF && docker compose up -d
control plane https://localhost:9080
agent :80 / :443
postgres :5432

A WAF you can read, audit and own

Every rule, verdict and log line stays in your infrastructure — under a license that lets you change any of it.